
The training content is divided into main topics that are covered through:
 Basics |  Attacks |  Defense |
• Adhering to camp rules, classroom conduct, and code of behavior.
• Introduction to cybersecurity (concept, importance, career paths: penetration tester, security analyst, security engineer, digital forensic analyst).
• Understanding cybersecurity teams (Red Team and Blue Team) and the CIA triad.
• Understanding hacking: types of hackers and the stages of their methodology.
• Understanding the concept of digital footprint and the impact of data leaks.
• Getting started on the TryHackMe platform.
• Applying encryption basics through the Caesar cipher.
• Introduction to Kali Linux and its use in cybersecurity.
• Executing basic commands to interact with the file system, understanding users and groups.
• Using flags and arguments to enhance command effectiveness.
• Copying and moving files and managing access permissions.
• Using terminal text editors such as Nano, and downloading files using wget.
• Introduction to Virtual Machines and their role in safe training environments.
• Understanding the difference between HTTP and HTTPS.
• Understanding how DNS works and its role in internet browsing.
• Understanding how web components interact (server, client, domain, etc.).
• Distinguishing between a vulnerability and its exploitation method.
• Hands-on exercises on the platform.
• Manual website auditing using browser developer tools only.
• Discovering methods to find unauthorized content and access hidden pages.
• Introduction to common web application vulnerabilities and their exploitation in a safe environment.
• Hands-on activities at each stage on the platform.
• Understanding password weakness and guessing methods.
• Using AI to build a Python tool that highlights this weakness.
• Understanding networking and internet fundamentals.
• Distinguishing between routers and switches, IP and MAC addresses.
• Reinforcing concepts through group competition.
• Understanding MAC spoofing and applying it practically.
• Comprehending ports, common protocols, and DNS/DHCP functions.
• Explaining network security concepts and types of cyber attacks.
• Mastering network and port scanning using Nmap.
• Using Wireshark to capture and analyze network traffic.
• Understanding risks of sending unencrypted data (HTTP vs. HTTPS).
• Learning about types of malware, distinguishing between hashing and encryption.
• Checking file reputation via VirusTotal. • Understanding DoS attacks and botnets.
• Understanding social engineering, phishing types, and fake pages.
• Identifying phishing email indicators.
• Securing accounts with strong passwords and password managers.
• Exploring OSINT tools for investigations and threat assessment.
• Understanding the defensive team and SOC analyst role, configuring firewall rules.
• Understanding SIEM systems, logging fundamentals, data sources and collection.
• Investigating alerts up to blocking malicious sources, and incident management.
• Applying tools in a complete attack chain through a CTF challenge.
• Developing security challenge-solving skills interactively.
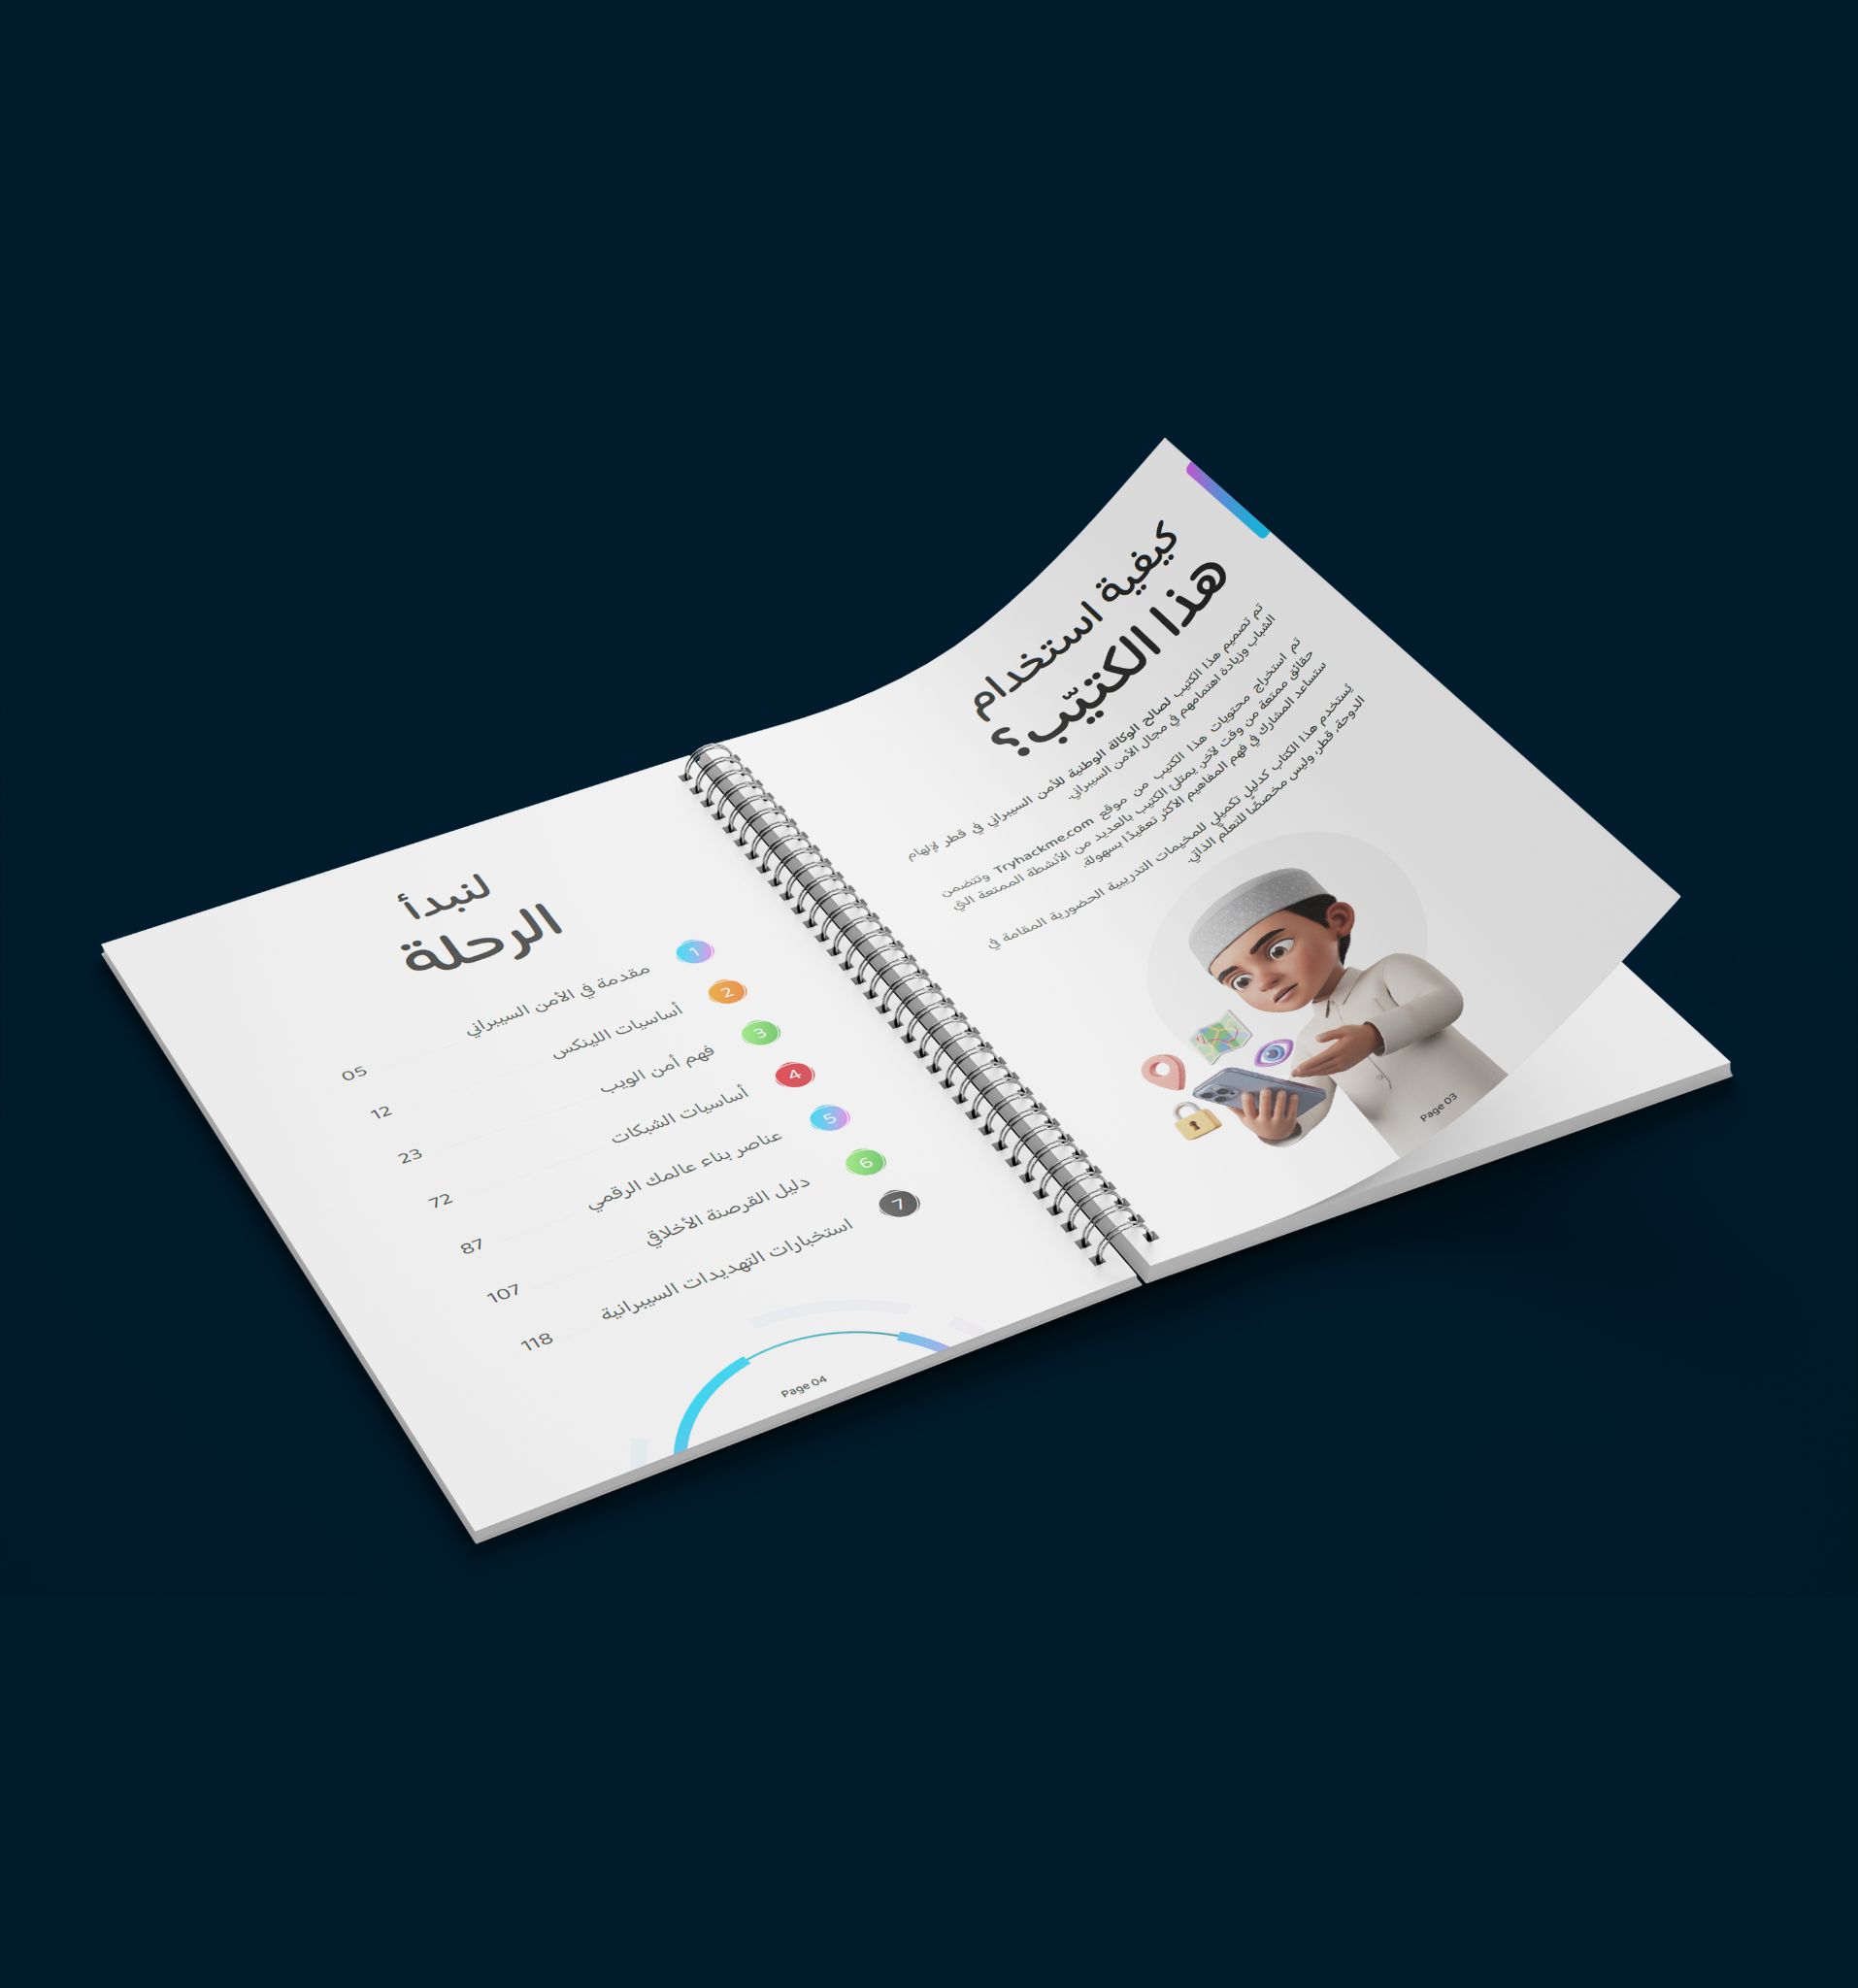
The Handbook A comprehensive booklet designed to contain all the content of the Cyber Security Camp, along with some fun activities. This booklet provides a comprehensive reference for participants, so they can retrieve valuable information, interactive activities, and interesting challenges they experienced during the camp.
|  |
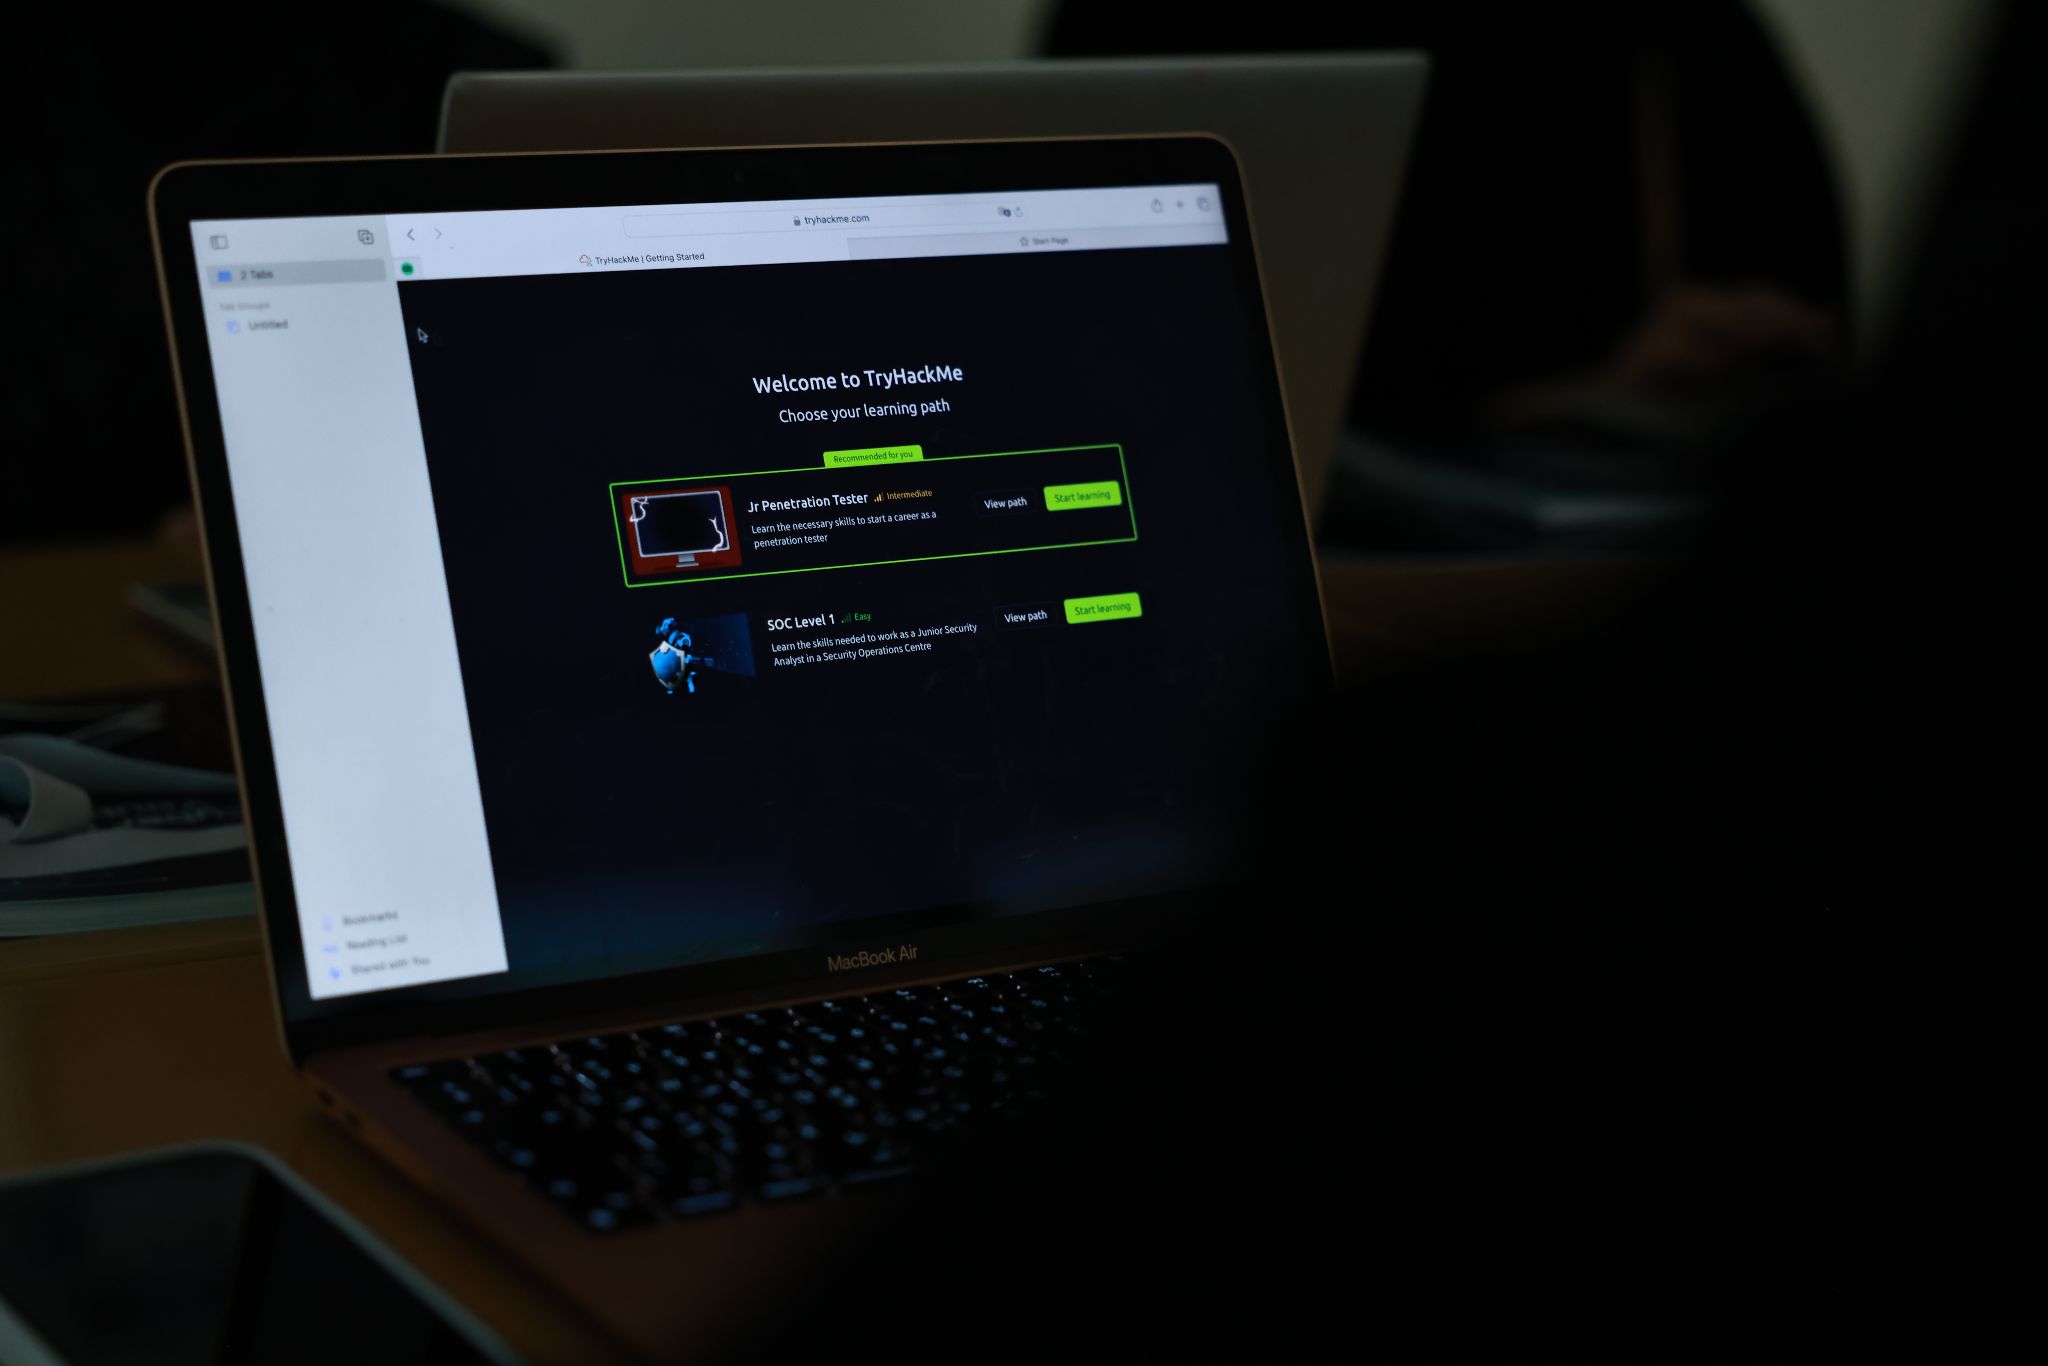 | TryHackMe Platform TryHackMe is an interactive learning environment designed to enhance cybersecurity skills through hands-on training. The platform offers virtual labs and interactive training courses, allowing users to gain hands-on experience in dealing with various cybersecurity scenarios. |
